Mirr Gov
AI that never crosses the boundary. Bundled for public-sector and sovereign environments.
Mirr Gov is designed around disconnected networks and air gaps, in-country data residency, local PKI and KMS, and an offline model catalog. Even with no external connectivity, the same execution harness, control, and audit evidence hold.
Review Mirr Gov- Confirm the identity and delegated authority of actors inside the boundary using local PKI.
- Judge data classification and permitted export against in-country residency rules.
- Select an approved sovereign model from the offline catalog with no external connection.
- Run only approved tools inside the disconnected network, stopping outbound attempts fail-closed.
- Preserve decisions and execution as tamper-evident evidence for audit and public accountability.
Before performance, you must decide where the data lives.
In public-sector and regulated environments, whether AI can be adopted is decided by the clarity of the boundary, not the length of the feature list. If data residency, network separation, supply chain, and audit accountability are not settled first, model quality is not even up for judgment. Tools built on the assumption of external connectivity cannot simply enter this environment.
Mirr Gov treats those constraints as the starting point rather than exceptions. Disconnected networks and air gaps, in-country data residency, local PKI and KMS, and an offline model catalog are the default. With no external connectivity, the execution harness, control, and audit evidence keep the same meaning. Functionality that would need to cross the boundary is excluded from the build rather than hidden at runtime.
A request to improve internal search completes without crossing the boundary.
“Find why internal search quality is dropping, propose an improvement, and run the relevant tests.”
- 01Verify identity inside the boundary
Confirm the requesting owner and the agent, and their delegated scope, through local PKI without relying on external identity.
- 02Judge the data class
Determine classification and permitted export against in-country residency rules, keeping sensitive data outside the default working boundary.
- 03Select a sovereign model
Choose only approved in-country models and tools from the offline catalog with no external connection.
- 04Execute inside the disconnected network
Edit code and run tests only in an approved isolated environment. Outbound attempts are not executed and are recorded.
- 05Evidence for public audit
Preserve decisions, execution, and outcomes as tamper-evident receipts for audit and disclosure obligations.
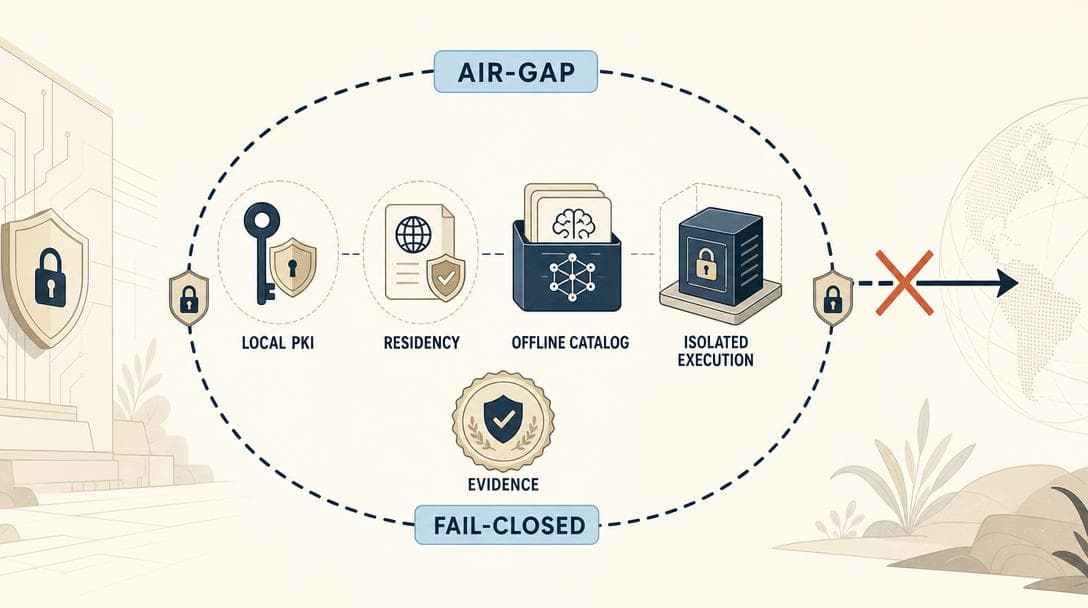
Sovereignty, network separation, provenance, and audit hold together in one deployment.
Data sovereignty
Fix residency rules and placement topology so data, prompts, and inference stay inside the national boundary. External transfer is blocked by default.
Disconnected and air-gapped operation
Model catalog, tools, and policy work locally with no external connection. When connectivity is absent, the system fails closed rather than open.
Supply chain and provenance
Only approved models and tools enter the offline catalog, and artifacts carry human and AI provenance. Unverified components are excluded from the build.
Accountable audit
Decisions and execution remain as tamper-evident receipts that anyone can verify later. Audit becomes signature verification, not log collection.
With no external connection, what Mirr Gov decides for every request.
Mirr Gov applies sovereign policy and disconnected topology to the same operating kernel. The sequence of decisions and the meaning of evidence match the enterprise setting, with a stricter boundary.
- 01local PKI · tenant · actor
Establish local identity
Confirm the person, service, or agent and its organizational context through local PKI, making the responsible actor explicit.
- 02residency · DLP · classification
Judge residency and export
Evaluate data class, residency requirements, exportability, purpose, and tool scope together.
- 03offline catalog · placement
Select a sovereign model
Choose an approved in-country model, tool, and location from the offline catalog without relying on an external catalog.
- 04air-gap · sandbox · fail-closed
Execute in the disconnected network
Execute only in an approved isolated environment; attempts to cross the boundary are not run and are recorded.
- 05decision · provenance · receipt
Seal the evidence
Retain allow or deny reasoning, execution result, and provenance as tamper-evident receipts.
Deploy to your level of network separation without changing the meaning of control.
These are deployment options, not claims of certification. Actual assurance scope is determined by institution-specific validation.
On-premises
Keep models, storage, and execution inside the institution’s infrastructure.
- In-country data residency
- Local PKI and KMS
- Internal audit integration
Disconnected
Operate in a network with external connectivity blocked, using an offline catalog.
- Offline model catalog
- Connectionless policy distribution
- External transfer blocked
Air-gapped · Sovereign
Operate on sovereign models and infrastructure in a physically separated environment.
- Sovereign models and infrastructure
- Build-time feature exclusion
- Fail-closed boundary policy
Prove that nothing left the boundary with evidence, not documents.
Mirr Gov evidence is part of the result, not a byproduct of control. Evaluations confirm the following items and their verification method against institutional requirements.
- Boundary
- Outbound call attempts and block records, and applied residency-rule outcomes
- Sovereign build
- Telemetry and external marketplace code physically excluded from the build
- Identity and authority
- Local-PKI identity, delegation scope, and allow or deny decisions with rationale
- Provenance
- Human and AI change provenance plus model, tool, and adapter versions
- Outcome
- Success or failure state, error, approval history, and receipt linkage
- Conformance
- Protocol conformance test results and control-item mapping status
※ A mapping capability; certification is the institution’s process.
Security invariants for teams evaluating a sovereign environment.
Mirr Gov is defined by the clarity of its boundary and failure behavior rather than a feature list.
Features excluded at build time
In the sovereign build, telemetry and external marketplace code physically do not exist. They are not hidden at runtime; they are absent by construction.
A boundary that closes on failure
If external connectivity or a required component is unavailable, the system closes rather than opens. There is no implicit fallback that bypasses the boundary.
Local trust root
Bind identity and signature verification to local PKI and KMS so verification needs no external dependency. Auditors verify signatures instead of trusting records.
Regulatory mapping and conformance
Track control items and evidence status for CSAP, ISMS-P, the Personal Information Protection Act, KISA secure coding, and the AI Framework Act and ISO 42001. Protocol conformance testing is part of the build and does not substitute for certification.
Review Mirr Gov against your boundary and audit obligations.
Tell us your network separation level, data residency requirements, local trust root, and required audit items, and we will confirm how far Mirr Gov operates inside the boundary.